
XSS at us7.admin.mailchimp.com and help.mailchimp.com

XSS at us7.admin.mailchimp.com and help.mailchimp.com

I found XSS at us7.admin.mailchimp.com 


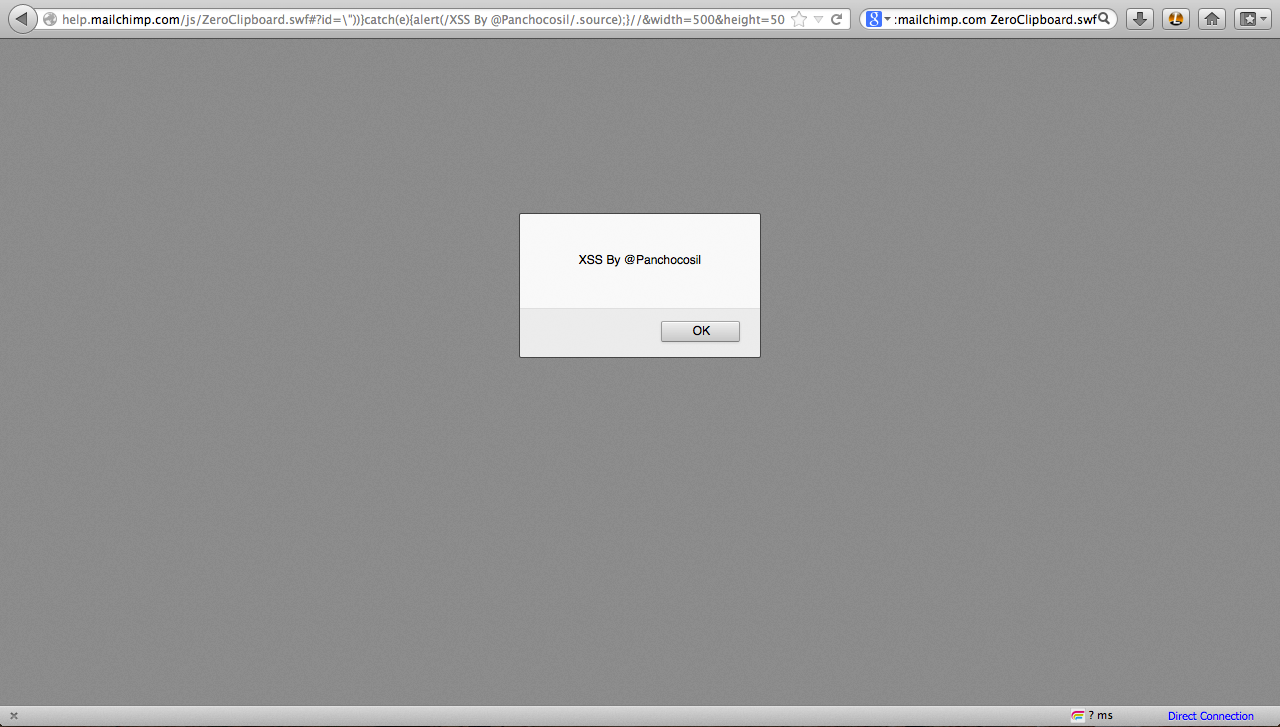
And an other Flash XSS at help.mailchimp.com


Report:Mon, Jun 17, 2013 at 12:46 AM
Fix:Tue, Jun 18, 2013 at 9:00 AM

Popular posts from this blog

One Cloud-based Local File Inclusion = Many Companies affected

Hi everyone, Today, I'm going to share how I found a Local File Inclusion that affected companies like Facebook, Linkedin, Dropbox and many others. The LFI was located at the cloud system of Oracle Responsys. For those who do not know Responsys is an enterprise-scale cloud-based business to consumer (B2C). Responsys gives every Business their own "private IP" to use the system in a private way. Business are not sharing IP with other companies.) How did I found this bug? Well as usual I was looking for bugs and I note that Facebook was sending me developer emails from the subdomain em. facebookmail.com. For example on my inbox, I had emails from fbdev@em.facebookmail.com This got me interested on the subdomain em.facebookmail.com and after a quick DIG I note that this subdomain was connected to "Responsys" which I had previously seen in other Pentests Responsys is providing em.facebookmail.com with the email services as you can see above. T...

Bypass Flash Same Origin Policy with Add-On

The same-origin policy is an important concept in the web application security model. The policy permits scripts running on pages originating from the same site. I found that users using FlashFirebug  are vulnerable to same-origin policy bypass. This Firefox add-ons create a files on the Flash Player Trust directory disallowing same-origin policy. For this example I will use Facebook Video preview box to trigger this Flash XSS. (Fortunately Faceboook use attachment.fbsbx.com ) By using a Flash XSS plus having FlashFirebug install on the Victim Firefox I can trigger this XSS and bypass Same Origin Policy I report this to Facebook and this was the response: And me as a good bounty hunter I report to Adobe: After doing a bit of looking I found that o-minds.com have a report bug page and here is their response:  I reply to them and after that I didn't receive a response. My conclusion: External Addons can bypass Flash "Same Origin Pol...

Store XSS on Shopping Express Checkout [Reward]

Google Shopping Express   is a same-day shopping service ("shop local stores online and get items delivered on the same day") from   Google   that was launched on a free trial basis in   San Francisco   and   Silicon Valley   in spring 2013 and publicly in September that year. This store XSS was showing at "Shopping Express Checkout" and by adding payload on the parameter "City" in wallet.google.com I could bypass restrictions and trigger this XSS back on Google Checkout. Image of Proof: This XSS was trigger just before paying pretty handy don't you think? Well I report this to Google Security Team and they reply very quick. Fixing this bug within a week: I'm very happy to be back on Google Hall of Fame and I like to thanks Google Security Team for the reward. I create a video reproducing this XSS: